
 Manufacturing
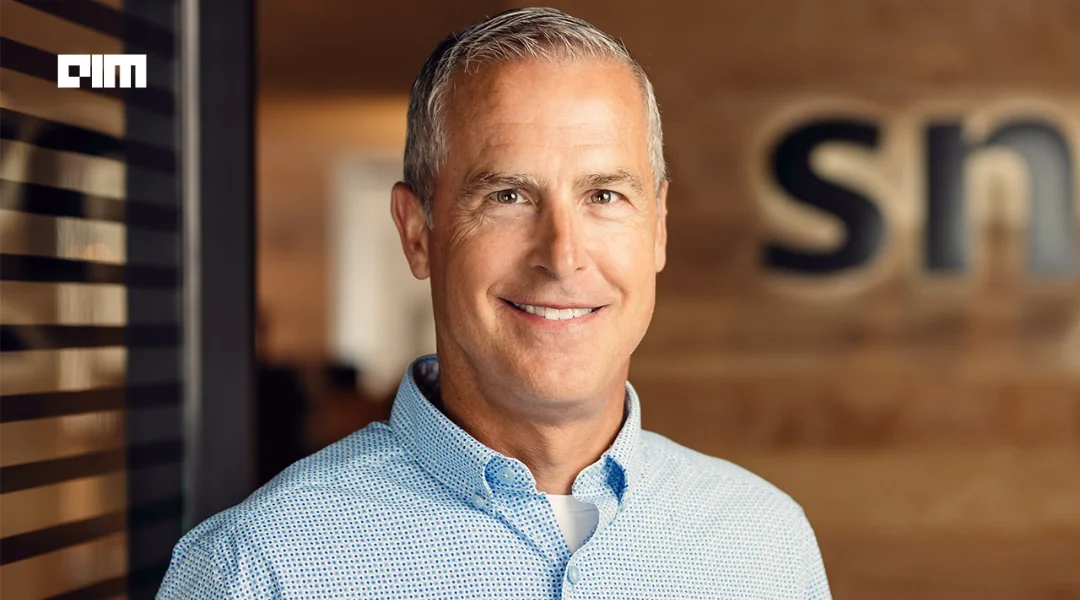
The software industry is producing code at an unprecedented pace, much of it thanks to generative AI. But this acceleration is accompanied by a sharp rise in security vulnerabilities, and many companies aren’t adapting fast enough. In a recent episode of Bloomberg Intelligence’s Tech Disruptors Podcast, Snyk CEO Peter McKay offered a grounded assessment of where cybersecurity is falling short and what organizations need to change if they want to stay protected.
“We’re in probably the most insecure phase of software development ever,” McKay said. According to him, developers are now writing 20 to 30 percent more code than before, but the output is 30 to 40 percent more vulnerable. AI coding assistants like GitHub Copilot, Windsurf, and Cursor, which generate code by learning from public repositories, are compounding the problem by reproducing outdated or insecure patterns. Developers may not understand or review what’s generated, and attackers are noticing.
The scale of the shift is substantial. Microsoft CEO Satya Nadella recently said AI is responsible for 30 percent of code in some company repositories, a figure expected to rise. While productivity gains are clear, McKay argues that the rapid adoption of generative tools has “put a strain on security teams trying to keep up.” The result is a widening gap between how fast code is written and how effectively it can be secured.
